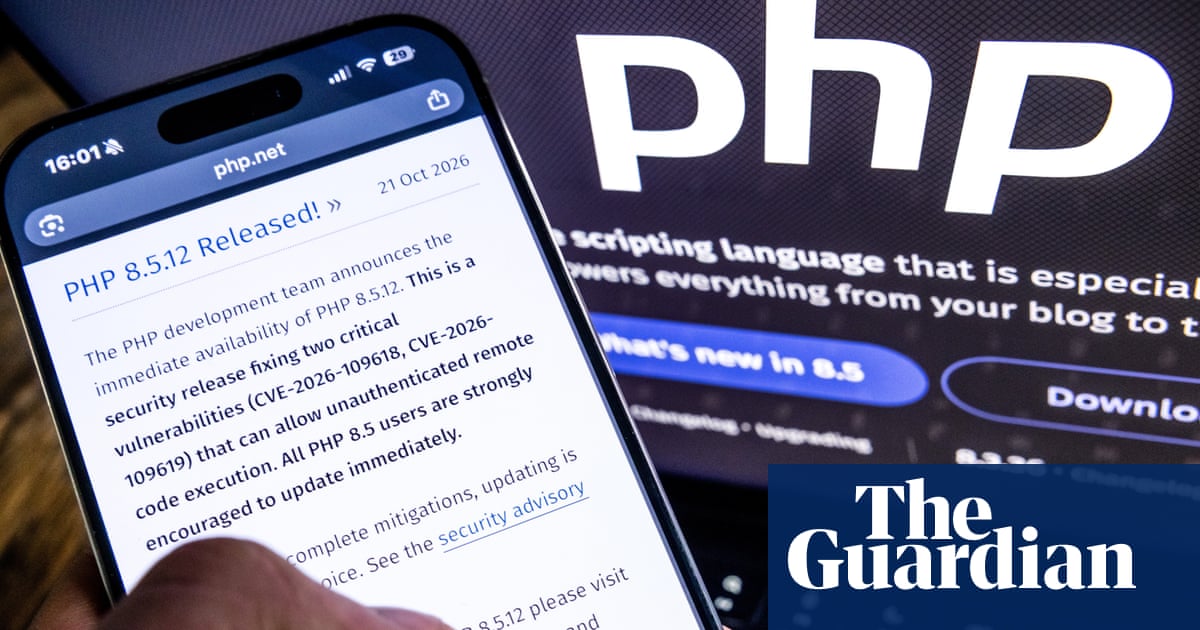
Flaw in PHP computer language leads to shutdown of websites around world
Websites around the globe have gone dark after a serious vulnerability was found in a computer language used to build much of the world wide web.
Belgian, Dutch, Finnish, French and German sites were among those that governments took down temporarily as they scrambled to patch the critical weakness in PHP, a language used by almost 70% of websites.
The vulnerability in the programming language, which became public on Tuesday, sparked warnings from national security agencies in Washington and London. It means millions of websites will need to be fixed. One internet infrastructure expert said Russian state actors or organised criminals could exploit the flaw to carry out cyber-attacks.
Wordpress, one of the most common website systems, uses PHP, as does Wikipedia, the messaging software Slack and – at least historically – much of Facebook. The Wikimedia Foundation said it had taken down several systems on Wednesday as a precautionary measure until they could be patched.
The organisation behind the language issued a patch on Wednesday after researchers testing cyberdefences discovered the flaw. The US National Security Agency told all organisations using PHP to take their systems offline if they were unable to patch them immediately. It said the vulnerability could “provide a direct path to the server’s file system or database”.
The UK’s National Cyber Security Centre gave similar advice and told organisations to check for “backdoors installed by an attacker”.
Because a fix is now public and AI tools are able to reverse engineer the bug with little effort, experts said they were bracing for a wave of intrusions as hackers jumped to get ahead of the updates.
AI was powering a “race to exploit”, said Costin Raiu, co-founder of cybersecurity research and incident response firm TLP:Black. He said the next step was the “mass compromise of every vulnerable web server on the internet”.
Prof Alan Woodward, a cybersecurity expert at Surrey University, said: “It was very surprising and troubling because of the extent to which PHP was used around the world. PHP issued a patch very quickly. The big thing is for everyone using it to get that in to make sure their systems are safe.
“The troubling part is there is going to be a long tail of websites who may not be maintained as well and they are going to remain vulnerable, which means we may see weeks and months of ongoing attacks. For the big juicy targets, I hope to goodness they are being patched quickly.”
Woodward said there was a window of opportunity for bad actors. “There is this race and some people unfortunately don’t even know they are in the race.”
OpenAI said it led a coalition of researchers that discovered the flaw and claimed “frontier AI” had been key. The researcher who found the weakness, however, said they used models available to the public.
Cybersecurity company Calif said in a blog post it found the flaws with the help of a large language model on 1 August and had been working on a fix ever since. Alphabet-owned cybersecurity company Wiz said in a blog post that it too had discovered it with the help of Wiz Atlas, its autonomous AI vulnerability research tool, as well as Google’s Gemini 4 Argon and OpenAI’s GPT-5.6 Sol.
The vulnerabilities remained hidden in the PHP codebase for more than a decade and would have been extraordinarily complicated for a human hacker to take advantage of, Wiz’s post said.
In a blog post late on Wednesday, Amazon security chief CJ Moses said its security team detected an attempt to exploit the vulnerabilities against one of its decoy “honeypot” systems on 17 October, four days before public disclosure.
skip past newsletter promotion
after newsletter promotion
The attempt on the system came from an anonymous internet address, suggesting the activity was conducted by a threat actor, Moses said, adding that it was unclear how the actor learned of the flaws while they were under embargo.
In a statement, the White House said it was made aware of the flaw on Friday.
In the UK, websites belonging to Edinburgh, Bristol and Oxford councils were taken offline. In France, local government websites including that of the Paris police prefecture went offline on Wednesday, as did in the Netherlands the national digital identity service, the website of the house of representatives and the site of the national cybersecurity centre.
The Australian Signals Directorate was temporarily affected by the outage overnight local time, with the national cyber defence agency noting other government websites may have been similarly affected.
Michał Woźniak, an internet infrastructure expert, said: “There’s going to be a lot of automatic exploitation of this.” The bug might allow cryptocurrency miners to exploit vulnerable servers at other people’s expense, he said.
He also said large crime organisations and Russian state actors could use the vulnerable sites as a launching pad from which to conduct distributed denial of service (DDoS) and other cyber-attacks.
The issue highlighted the poor state of internet infrastructure, Woźniak said, something that was being brought to light by advancing AI models but that had been a long-developing problem. The underlying vulnerabilities the researcher found were decades old.
“This is an environmental problem in an industry where there’s an incentive to move fast and make changes,” he said. “There’s an incentive to deploy a thing and then never update it and not think about maintenance.”
Originally published by theguardian.com. Syndicated material does not necessarily reflect the views of Grazia British.
More Culture
European air fares could rise by as much as 20% in 2027, Ryanair boss predicts
Conflict in Middle East is pushing jet fuel costs higher and many carriers are not hedged against such increases, Michael O’Leary says
Electricity costs put UK steelmakers in worst position in three years against EU rivals
Premium paid over French counterparts has risen to almost £30 a megawatt hour, analysis by lobby group finds
Why Britain should reject the lure of cheap – and scary – Chinese AI
In the west the technology comes with at least some effort to provide security and a benign intent – not so from China
The water torture goes on at Thames. Sector-wide reform isn’t moving much faster | Nils Pratley
If ‘public control’ bit is delaying overhaul, that needs to be nailed down sharpish or continued uncertainty could be costly